CVE
Follow from the Fediverse
Follow #cve from Mastodon or any other Fediverse app and its public posts arrive in your timeline. No vutuv account needed.
@cve@tags.vutuv.de
Posts with this tag
11 posts
Filters

Every panel I go on: “Gina but isn’t open source inherently less secure than closed source?”
Meanwhile, MS Paint does remote code execution now 💀

On October 20 and 21, an attacker tried to exploit CVE-2026-97229 against Alpine Linux’s GitLab instance.
We have found no evidence that it succeeded, but we cannot rule it out, so we treated the instance as compromised and rebuilt it from scratch. Our checks show that the aports repository, packages, and the October 21 releases were not tampered with.

📣 Updated PHP Windows builds are now available:
- PHP 8.2.35-1
- PHP 8.3.36-1
- PHP 8.4.27-1
- PHP 8.5.12-1
‼️ These builds include Brotli 1.2.1 to fix CVE-2026-111497, an out-of-bounds write in Brotli decompression. This vulnerability is in the bundled Brotli library, not PHP code.
📝 Read more: php.net/archive/…

PHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell Patches
PHP warns CVE-2026-115560 may enable code execution in unusual session setups and advises disabling session upload progress pending a routine fix.
Oh, the story continues…
📣 Announcing the immediate availability of:
- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12
‼️ These address the following critical security issues:
- Remote Code Execution via Out of Memory corruption (CVE-2026-109618)
- Remote Code Execution via Stale Global State (CVE-2026-109619)
📝 php.net/ChangeLog-8.php
🎁 php.net/downloads?source=Y
Windows: php.net/downloads.php?os=windows
Read more: php.net/archive/…


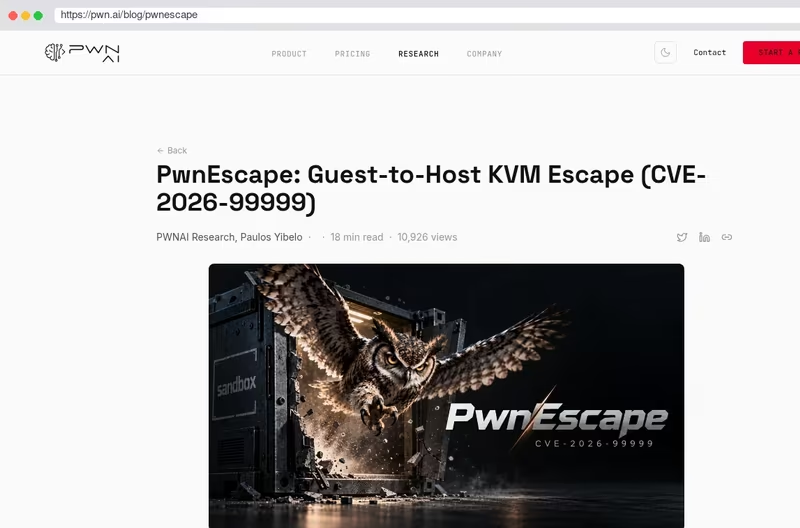
Heads up for fellow Linux admins: CVE-2026-99999 (dubbed “PwnEscape”) is out, and it is a nasty one (CVSS 9.3).
Despite being called a KVM escape, the actual bug lives in the host IPv4 networking stack. Untrusted CHECKSUM_PARTIAL offload metadata from a guest can overwrite already-validated packet headers during ip_do_fragment(), leaking host memory or allowing a guest-to-host escape.
Mainline patches landed Oct 14, and stable backports are out. Check your hypervisors and reboot!

From @mold@infosec.exchange’s keynote: The avalanche of security reports from #OpenSSL’s point of view: from 9 reports a months to 70.
OpenSSLCon26
CVE


1313 Kernel-CVEs: Wenn die Sicherheitslücke zum Normalfall wird
linuxnews.de/1313-kernel-cves-wenn-die-… #kernel #ki #cve #linux #linuxnews